Phase Gate Manager runs on Cloudflare, Supabase and Resend — all three SOC 2 Type 2 compliant. Our own SOC 2 audit is on the roadmap; we don't claim what we haven't earned.
Ongoing Security Testing
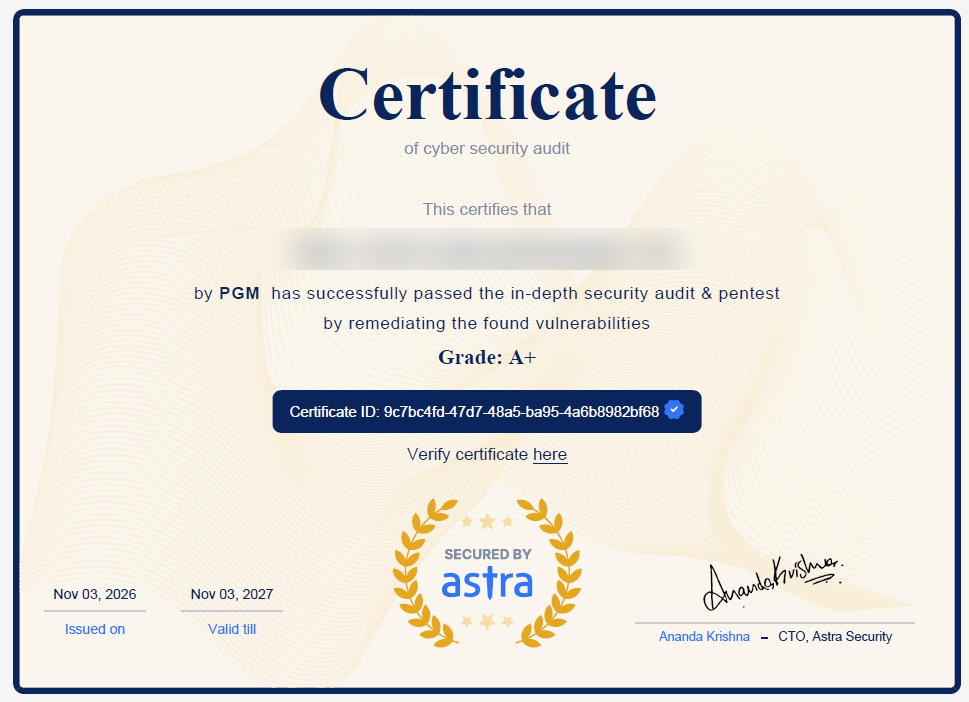
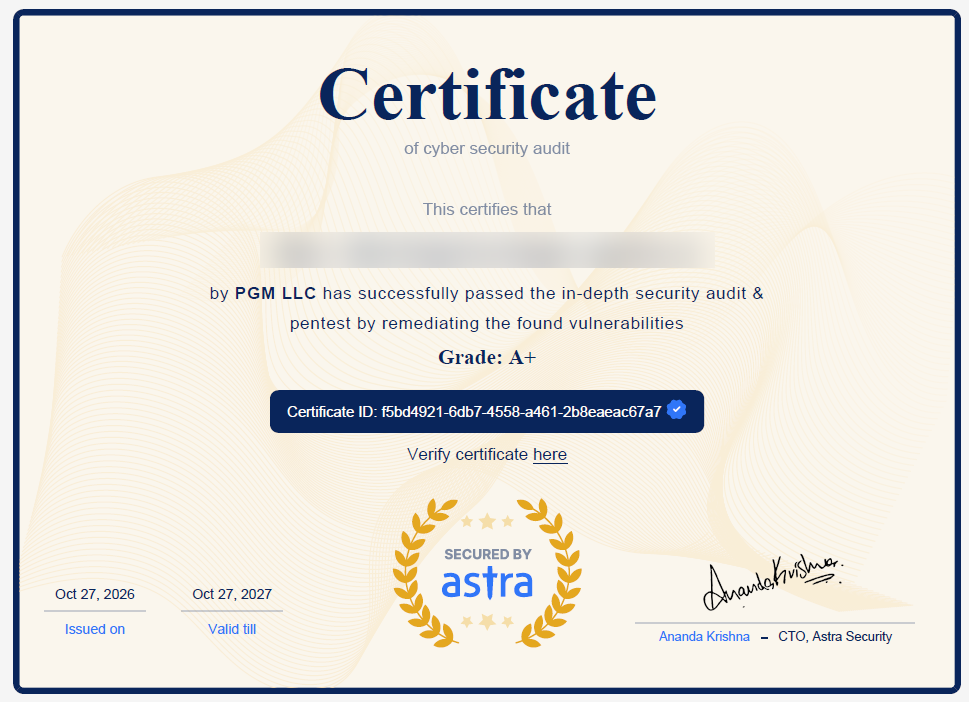
Automated vulnerability scans run on a schedule and before each new instance is deployed. Annual human-led penetration testing by Astra Security. Full report available to qualified prospects under NDA.
Customer-Hosted
Your data lives on your Supabase project, behind your Cloudflare zone, and your notifications go out through your own Resend account. We don't host it. We can't see it without your explicit consent. If you ever stop working with us, you keep your data, your install, and your audit trail.
Audit-Ready Documentation
Every gate approval, every change, every access — captured to a permanent audit log that can't be modified or deleted, even by administrators. Comprehensive enough to support internal reviews, customer audits, or regulatory inquiries. FDA 21 CFR Part 11 electronic signature support is on our roadmap. We tell you what's available today, not what's coming.
Defense In Depth
Cloudflare WAF with OWASP Core Ruleset, Page Shield, Leaked Credentials Detection, and Super Bot Fight Mode — provisioned on every instance during setup. Supabase Row-Level Security on every table, with MFA step-up enforced at the database, not just the login screen. Account creation handled server-side; no self-registration. Turnstile on sign-in. Per-instance origin allowlist on every backend function. Encrypted at rest and in transit. Multiple layers, none of them optional.
Multi-Factor Authentication
Multi-factor authentication on every account, built on the TOTP standard — so it works with any authenticator app your team already uses, such as Google Authenticator, Authy, or 1Password. Layered on top of role-based access control across six customer permission levels, plus per-person confidential and financial visibility, and Supabase Row-Level Security enforced at the database layer. On by default, not an upsell.
Vendor-Pushed Security Patches
Customer-hosted doesn't mean you're on your own when a vulnerability emerges. Security patches deploy to your infrastructure automatically through our private repo connection. The benefits of self-hosting, the convenience of SaaS-style updates.
Layer by Layer
A request crosses every layer — edge, transport, identity, database — before it reaches your data.
Questions Worth a Real Answer?
Talk to a practitioner about the security architecture, deployment model, or specific compliance questions for your environment.